Back to Overview
06 / 06
PROJECT 06•commerce cro

Cafe Raz Specialized Commerce

High-Converting Single-Product Coffee Platform with Dynamic Blend Calculator

Live Subdomain DemoView on GitHub

Technologies & Stack

Next.js 16React 19TypeScriptPrisma ORMPostgreSQLTailwind CSS v4Framer MotionZod
caferaz.parsadevstudio.ir
IDLE
Cafe Raz Specialized Commerce

System Overview & Purpose

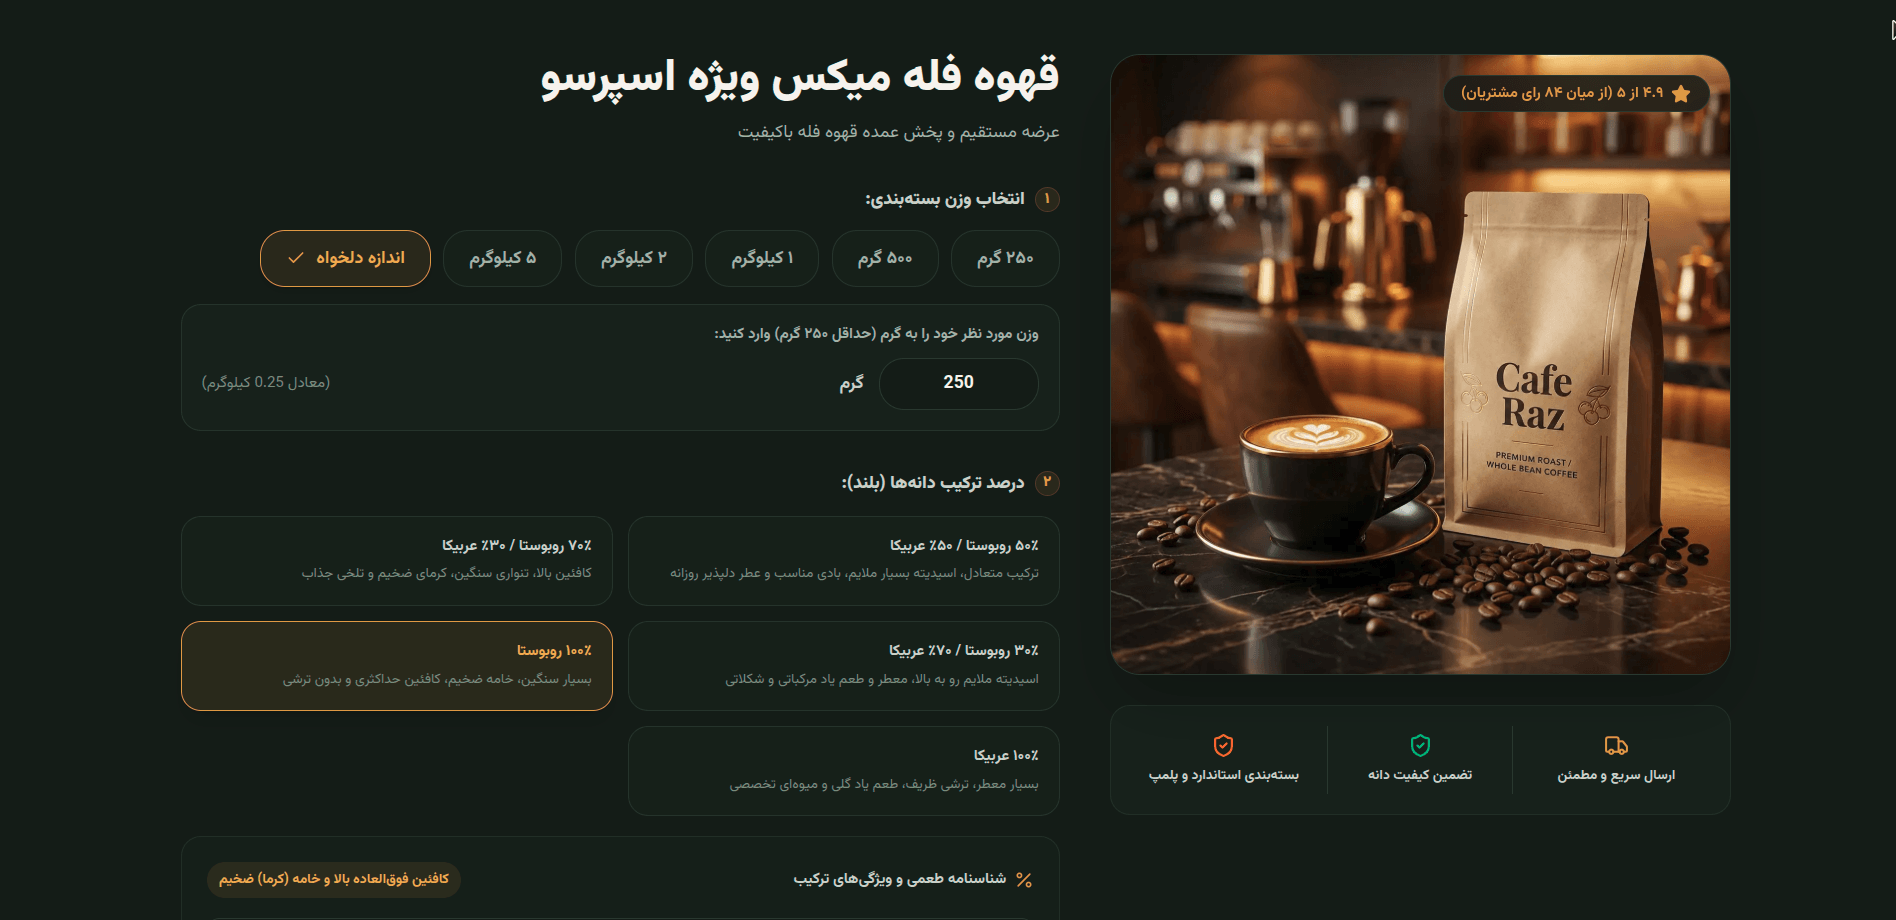
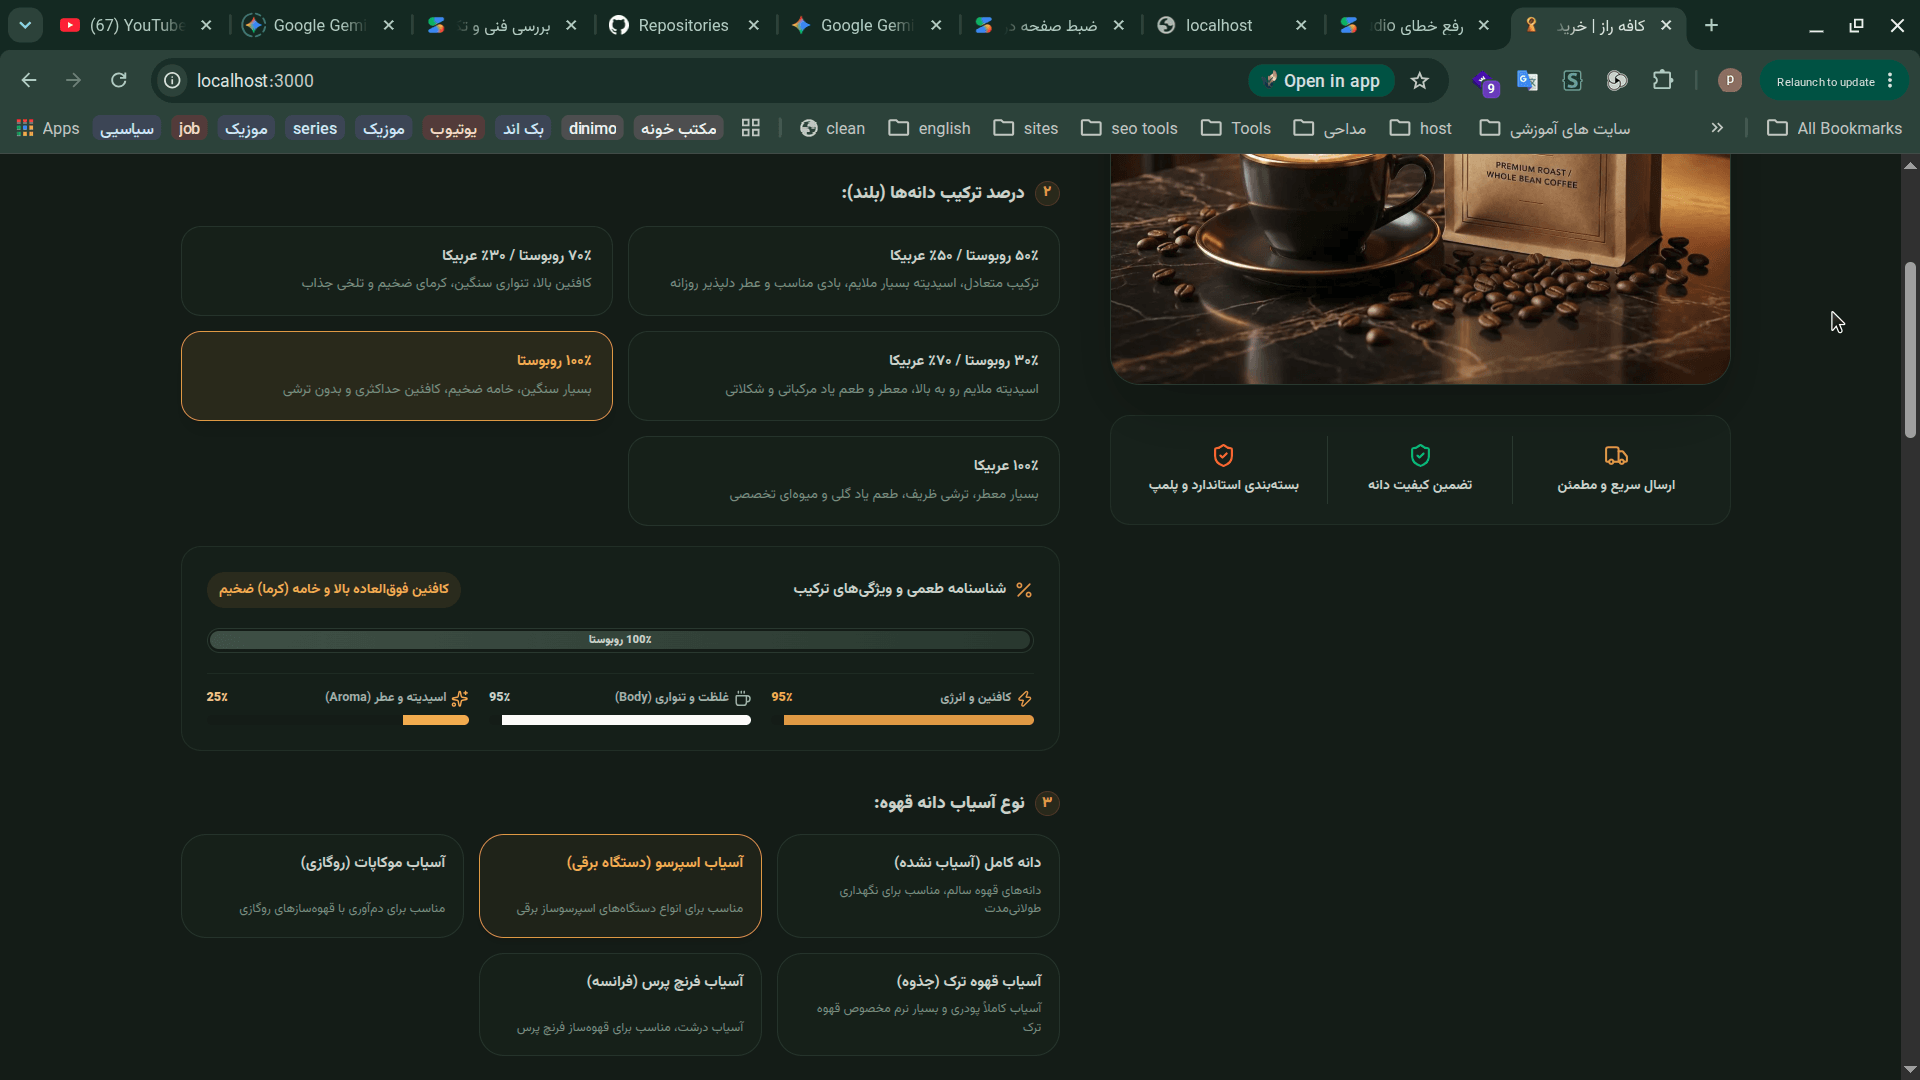
Specialized e-commerce experience focused on custom coffee bean formulations, real-time sensory profile simulation, anti-brute-force SMS OTP verification, and custom signed session security.

Core Architecture

Next.js 16 Server Actions orchestrate purchases and coupons without REST API bloat. Session integrity secured via HMAC-SHA256 signed cookies and timingSafeEqual defense.

Performance Benchmarks

HMAC-SHA256

Security Layer

Custom signed session cookies with constant-time verification

Server Actions

Checkout Latency

Zero external API latency with direct database mutations

Optimistic UI

UX Interaction

Instant feedback on comments and coupon evaluations

Engineering Challenges & Solutions

Real software roadblocks encountered during production and their architectural resolutions.

01.

Scoped Token Architecture with Constant-Time Guard

The Problem: Heavy external authentication libraries added unnecessary bundle size for a focused consumer checkout funnel.
The Architectural Solution: Built lightweight HMAC-SHA256 scoped session tokens (admin, user, form) with constant-time equality validation (crypto.timingSafeEqual) eliminating timing attacks.
Scoped Token Architecture with Constant-Time Guard — Source Solutiontypescript
123456789101112131415// Scoped session token verification with constant-time equality check (timing safe)
export function verifyScopedToken(expectedScope: SessionScope, token: string): string | null {
  const [rawPayload, signature] = token.split('.');
  const hmac = crypto.createHmac('sha256', SESSION_SECRET);
  hmac.update(rawPayload);
  const expectedSignature = hmac.digest('hex');

  const sigBuf = Buffer.from(signature, 'hex');
  const expBuf = Buffer.from(expectedSignature, 'hex');
  if (sigBuf.length !== expBuf.length || !crypto.timingSafeEqual(sigBuf, expBuf)) {
    return null; // Cryptographic tampering detected or timing attack blocked
  }
  const [scope, payload] = rawPayload.substring(0, rawPayload.lastIndexOf('|')).split(':');
  return scope === expectedScope ? payload : null;
}
02.

Multi-Vector Anti-Brute-Force OTP Gate in PostgreSQL

The Problem: SMS verification gates face denial-of-wallet abuse and credential stuffing without external Redis infrastructure.
The Architectural Solution: Engineered in-database throttling tracking hourly IP quotas, phone attempt records, mandatory 120s cooldowns, and automatic code invalidation after 5 failed attempts.
Multi-Vector Anti-Brute-Force OTP Gate in PostgreSQL — Source Solutiontypescript
12345678910111213141516171819// In-database layered OTP verification & brute-force invalidation via Prisma
export async function verifyOtpInternal(phone: string, code: string): Promise<boolean> {
  const record = await prisma.otpRecord.findFirst({
    where: { phone: phone.trim(), used: false, expiresAt: { gt: new Date() } },
    orderBy: { createdAt: 'desc' },
  });
  if (!record || record.attempts >= 5) return false;

  if (record.code === code) {
    await prisma.otpRecord.update({ where: { id: record.id }, data: { used: true } });
    return true;
  }
  const nextAttempts = record.attempts + 1;
  await prisma.otpRecord.update({
    where: { id: record.id },
    data: { attempts: nextAttempts, used: nextAttempts >= 5 }, // Invalidate on 5th failed try
  });
  return false;
}

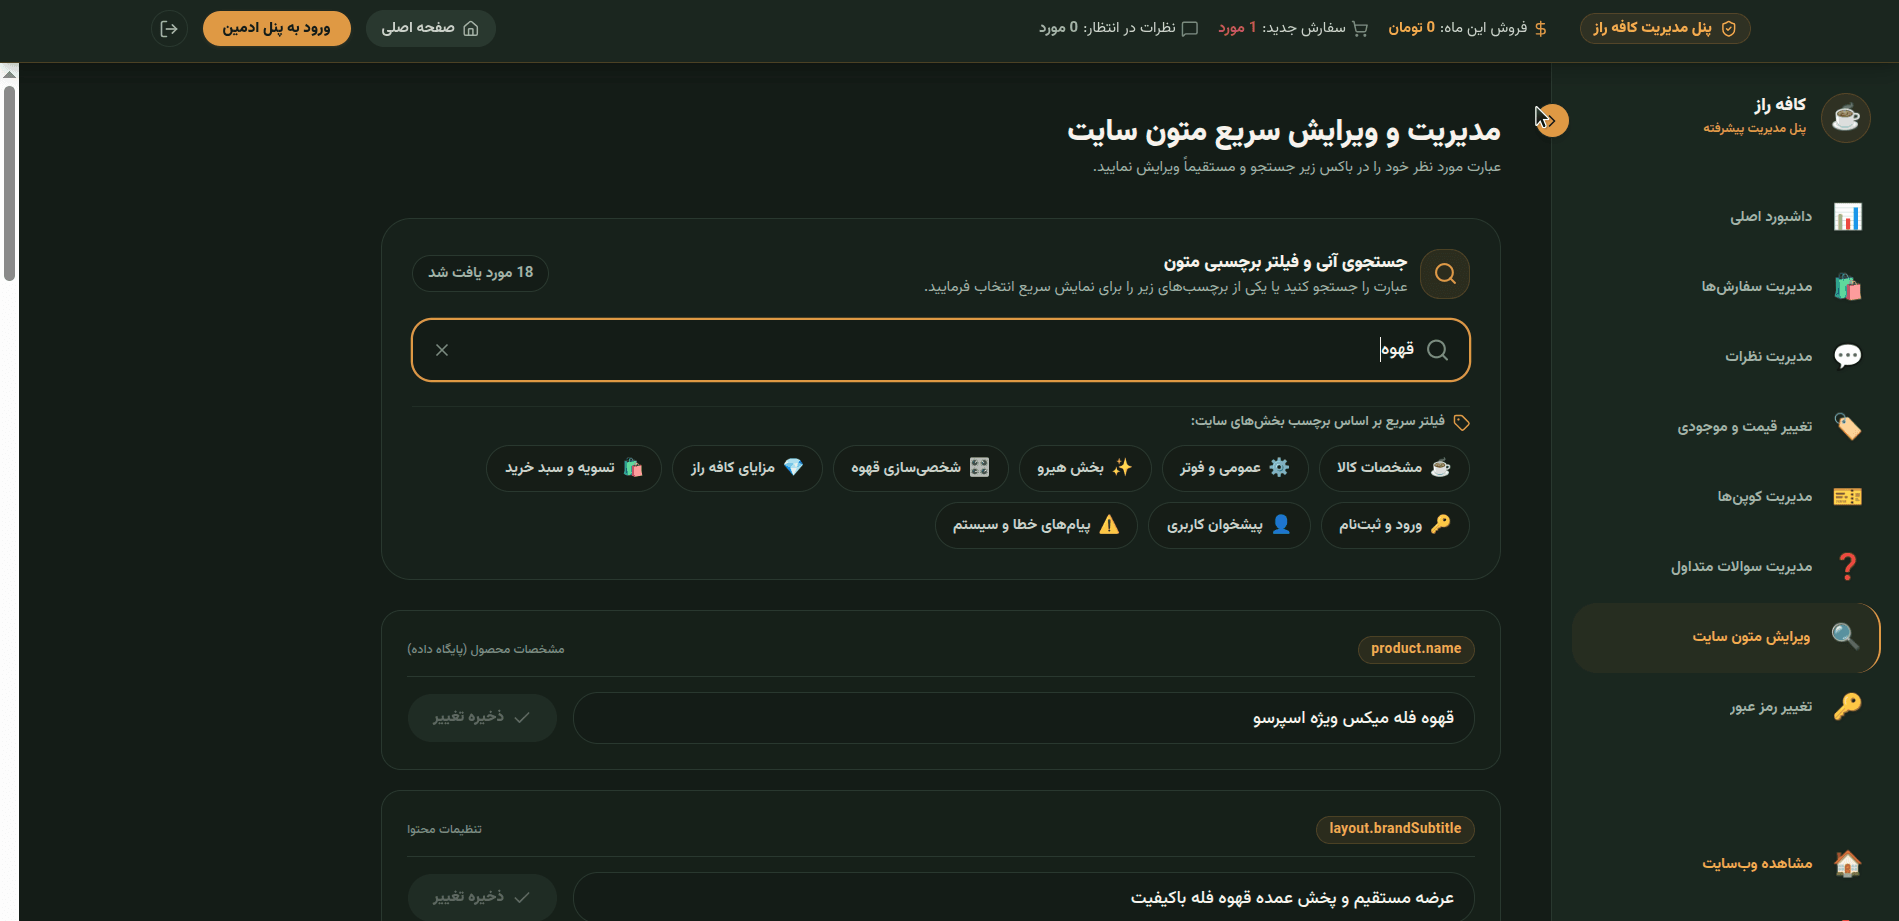
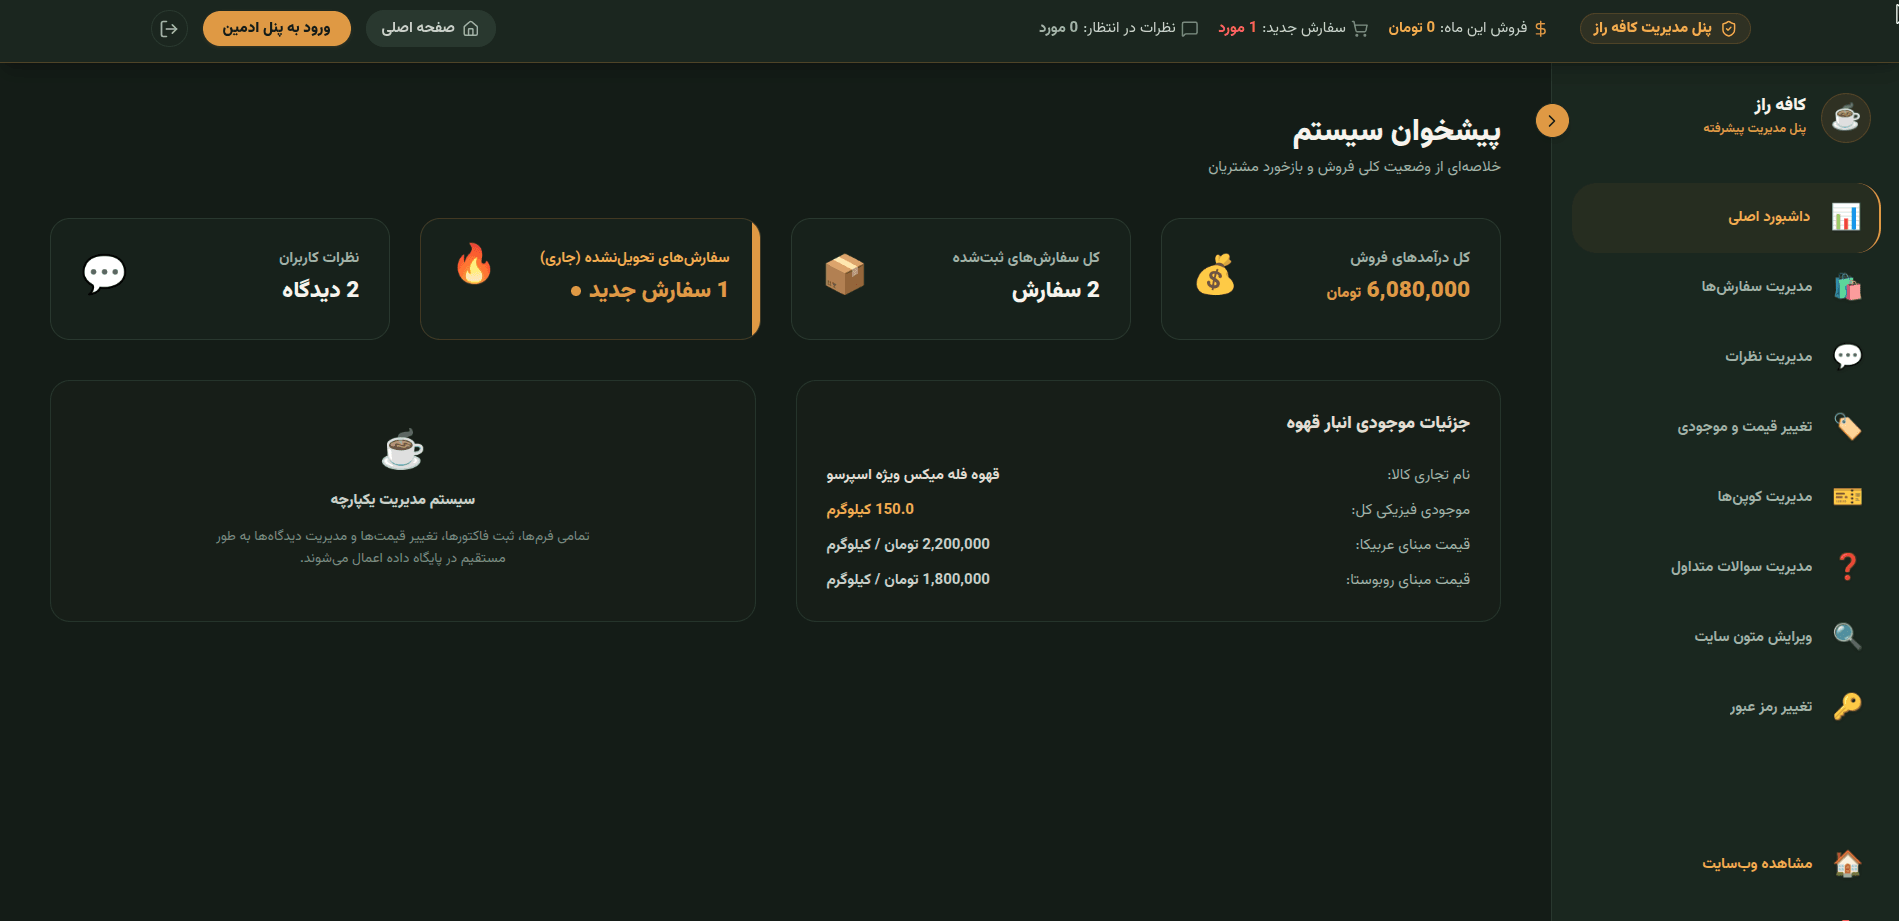
Interface & System Screens

High-resolution captures of the live interface and management panels.

Cafe Raz Specialized Commerce Screen 1
01
Cafe Raz Specialized Commerce Screen 2
02
Cafe Raz Specialized Commerce Screen 3
03
Cafe Raz Specialized Commerce Screen 4
04
Previous System
Vita Personal Engine
Back to Overview